Captured, not generated.
Tamper-evident photo evidence for disputes, audits and compliance. Captilo gives insurance, construction and legal-ops teams a defensible photographic record — sealed at capture, independently timestamped, verifiable by anyone.
- eIDAS qualified timestamp
- C2PA conformant
- Photos stay on the device
- Servers in Germany
Free for 2 months, up to 50 people. Android now, iOS coming soon.
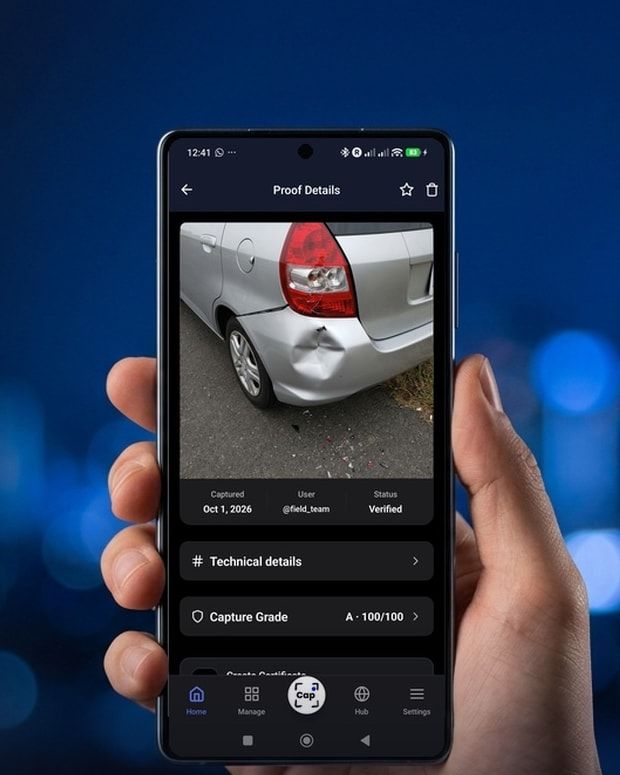
A photo is no longer proof on its own.
AI can fake any photo in seconds. Standard EXIF metadata — the time and place stored in an image — is stripped or rewritten with free tools in seconds. When a claim, a handover or a milestone depends on a photo, "trust me" is not a record.
- Generated AI produces convincing images on demand.
- Edited Metadata can be rewritten after the fact.
- Backdated Today's photo, presented as last week's.
Three steps from shutter to proof.
-
Capture
Take the photo in Captilo. Time, place and device are recorded at the moment of capture, behind a biometric or PIN gate.
-
Secure
Within seconds, a SHA-256 fingerprint is signed on the device and recorded on a public blockchain (Sonic). APED, a trust service provider on the EU Trusted List, issues an eIDAS qualified timestamp.
-
Share
Send the photo with its certificate PDF. Anyone can check it at captilo.app/verify — no account, and without needing Captilo.
Under the hood: SHA-256 hashing · device signature (secp256k1) · single-use 60-second nonce against backdating · Google Play Integrity device attestation · rooted devices and mock locations flagged · on-device screening for screen/print captures, photo swaps, location integrity and emulators · capture grade A–D
Built for work where photos get disputed.
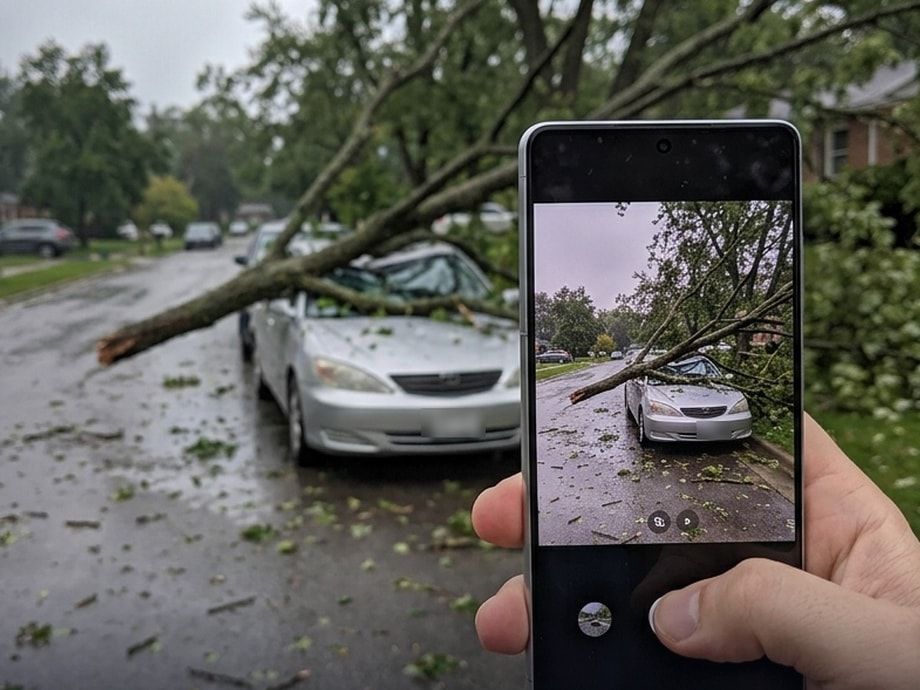
When it really happened, prove it.
- Policyholders, adjusters and field staff record damage with sealed time and place — ready for the claim file.
- Backdating is blocked at capture: every proof needs a single-use, 60-second nonce.
- Claims handlers verify the certificate at captilo.app/verify — no account, no extra software.
Also used for
Property & rentals
Record condition at move-in and move-out, so deposit and damage disputes start from the same evidence.
Construction
Document hidden work before it's covered, and milestones as they're reached.
Legal & disputes
A tamper-evident photographic record with an independent qualified timestamp.
Supply chain & delivery
Capture the condition of goods at pickup and drop-off.
Audits & field monitoring
For site inspections, NGOs and third-party monitors: a record of where and when each photo was taken.
- Organisation accounts
- Proof requests with four-eyes confirmation
- Certificates that attach to claims, procurement and case-management workflows
- Programmatic verification against the blockchain registry — no SDK needed
Proof you can check without trusting us.
eIDAS qualified timestamp
Issued by APED, a trust service provider on the EU Trusted List.
C2PA conformant
Captilo is a C2PA Conformant Generator Product (Assurance Level 1), aligned with the open Content Credentials standard.
Public blockchain
Proofs are anchored on Sonic and stay verifiable even if Captilo ceased to exist.
Privacy by design
Photos stay on the phone. Our servers in Germany never receive photos, names or locations. GDPR-aligned design.
Device integrity
Google Play Integrity attestation, flags for rooted devices and mock locations, and a capture grade from A to D.
An ordinary photo vs. a Captilo record.
| Ordinary phone photo | Captilo | |
|---|---|---|
| Time & place | Stored in EXIF, editable in seconds | Sealed at capture, signed on the device |
| Changes after capture | Not detectable | The file no longer matches its recorded fingerprint |
| Independent time | None | eIDAS qualified timestamp |
| Fraud signals | None | On-device screening + grade A–D |
| Who can verify | You trust the sender | Anyone, at captilo.app/verify, no account |
- Private by default No photo upload — the image stays on the device.
- Vendor-independent The proof outlives us: public chain + EU trust service.
- Fits your workflow PDF certificate plus programmatic checks.
Questions buyers ask us.
Is a Captilo record admissible in court?
We don't make that claim. Courts decide admissibility, depending on jurisdiction and case. Captilo gives you a tamper-evident record: a fingerprint signed on the device, anchored on a public blockchain, plus an eIDAS qualified timestamp. The eIDAS presumption covers the timestamp's date and time, not the authenticity of the photo. Your counsel can judge how it fits your process.
Can Captilo catch every fake or staged photo?
No tool can. Captilo makes changes after capture detectable and blocks backdating with a single-use 60-second nonce. It also screens on the device for common tricks — photographing a screen or print, photo swaps, location spoofing and emulators — and gives each capture a grade from A to D. It cannot prove who took the photo or that a scene wasn't staged.
Do you store our photos? What about GDPR?
No. Photos stay on the phone. Our servers in Germany never receive photos, names or locations. The design is GDPR-aligned.
What if Captilo stops operating?
Your proofs stay verifiable. They are anchored on a public blockchain, and the qualified timestamp comes from an independent EU trust service provider. Neither depends on us.
What do we need to start, and how does it fit our systems?
Android phones today; iOS is coming soon. Certificates are PDFs that attach to your claims, procurement or case-management workflows. Proofs can also be checked programmatically against the blockchain registry, with no SDK needed. The pilot is free, and we agree ongoing terms with you during it.
Run a free pilot with your team.
Two months, up to 50 people, 3,000 shared credits — free, and extendable once by a month.